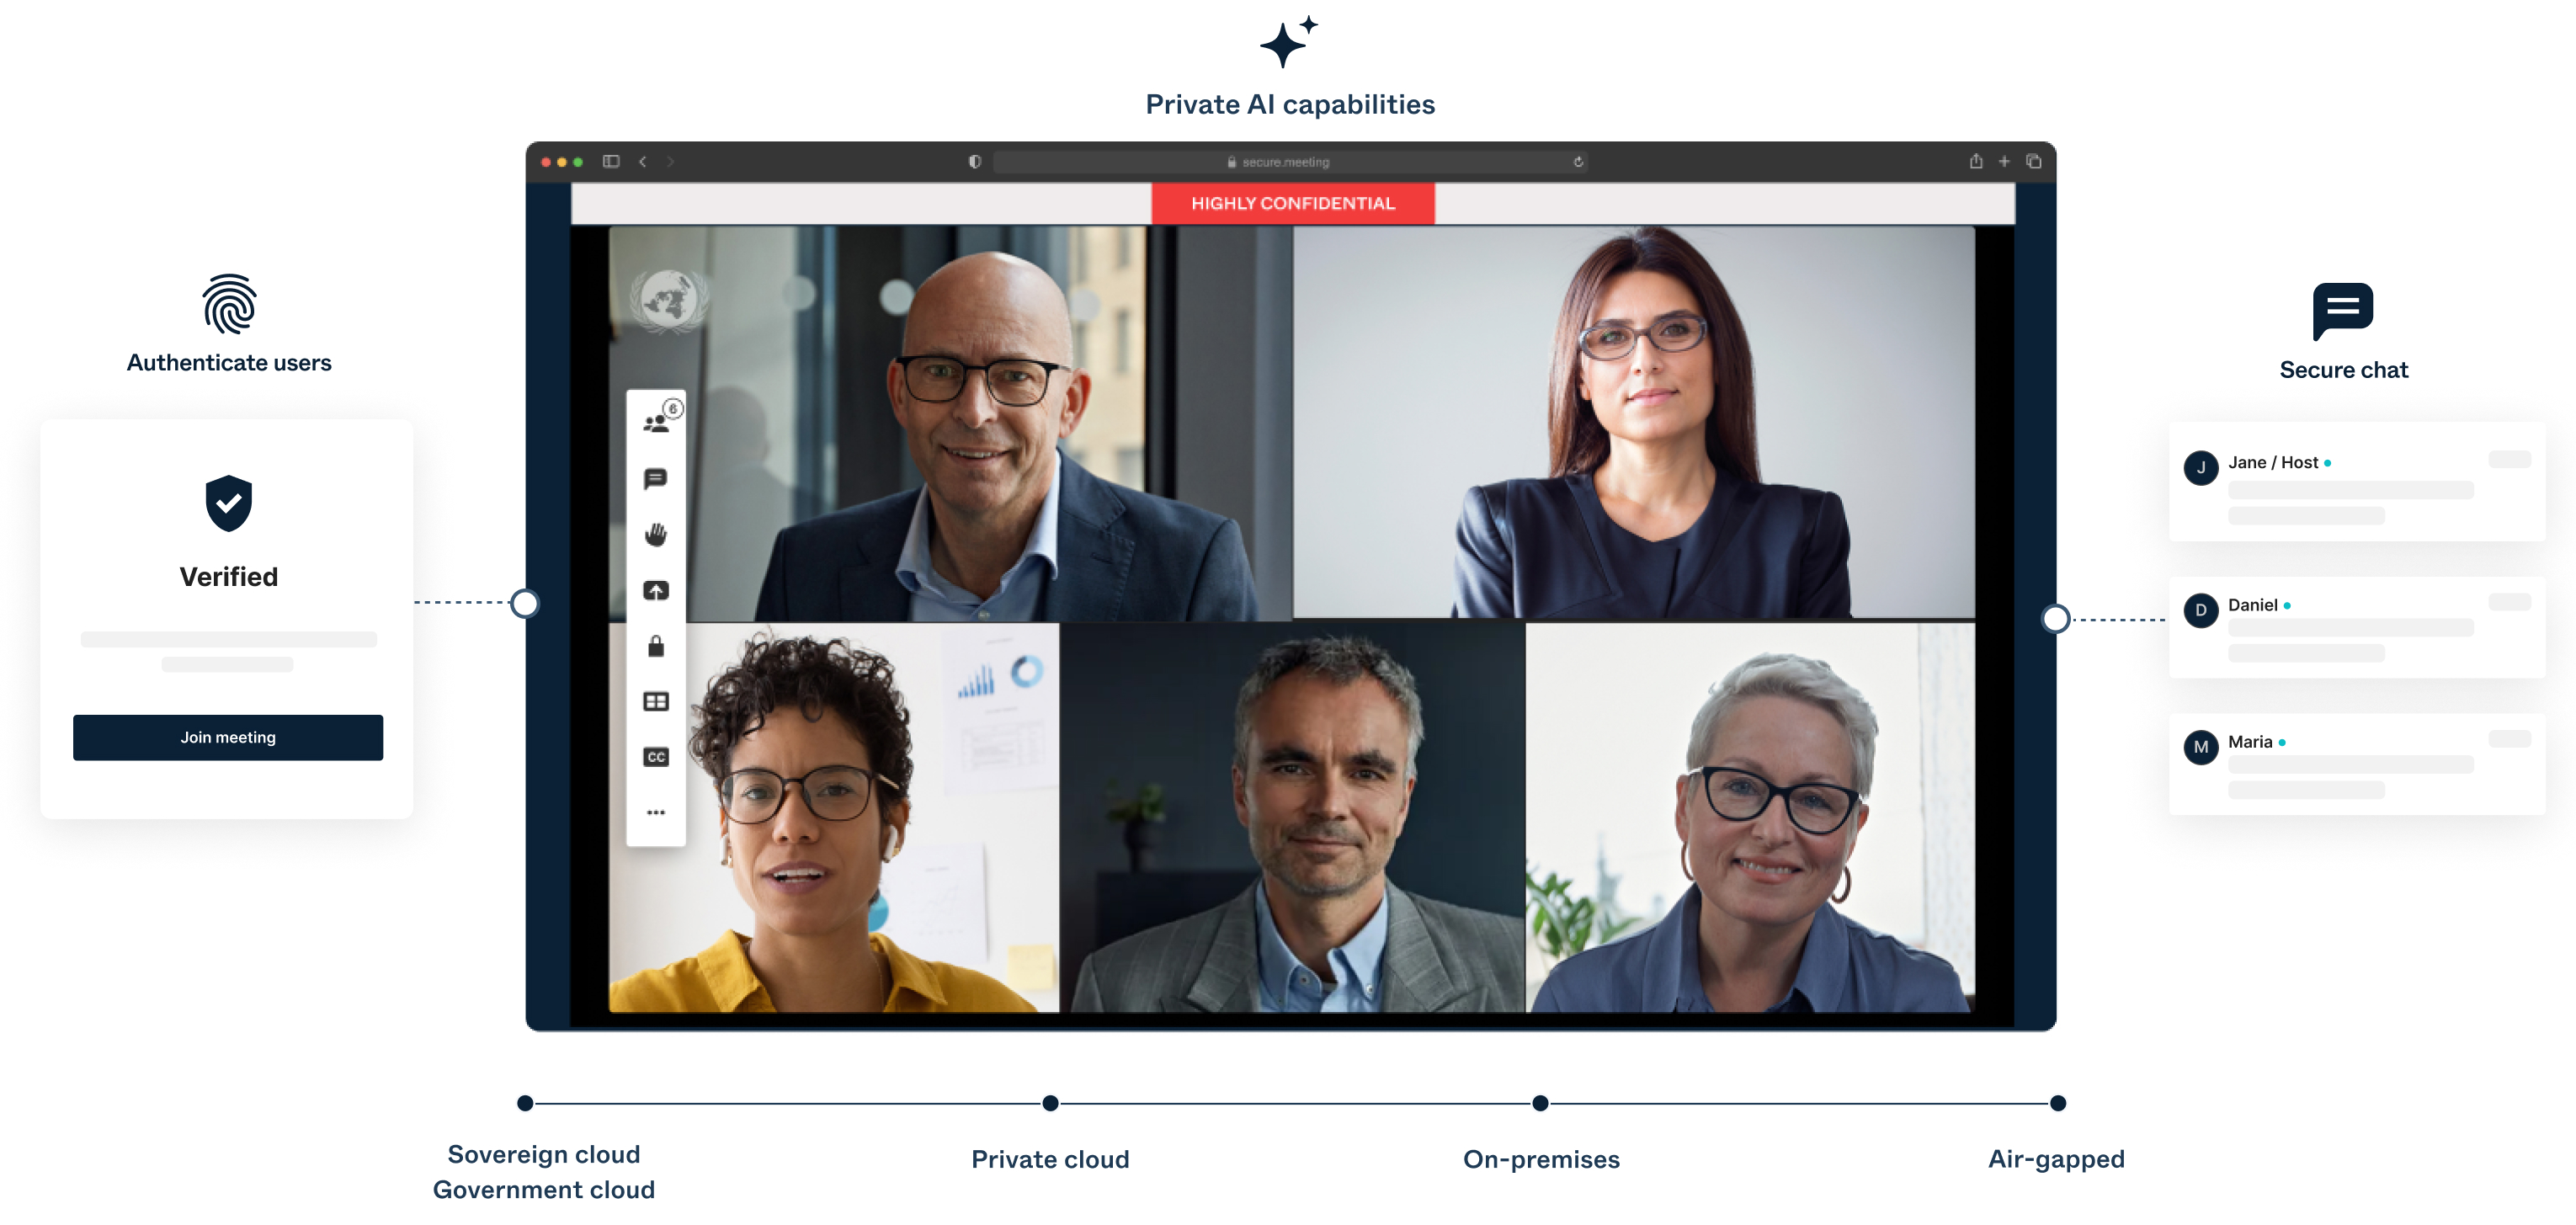
1. Understanding modern access control
Every organization has conversations that require a different level of protection.
A routine team meeting doesn't need the same safeguards as a defense planning session, a healthcare consultation, a financial review, or a discussion involving sensitive government information. Whether people are communicating through voice, content sharing, or video, the challenge is making sure the level of access control matches the sensitivity of the information.
Video data is data. A video session can capture not only what is being discussed, but also who is participating, how decisions are made, and the context behind those decisions. Protecting that information means controlling who can access it and what they are allowed to do with it.
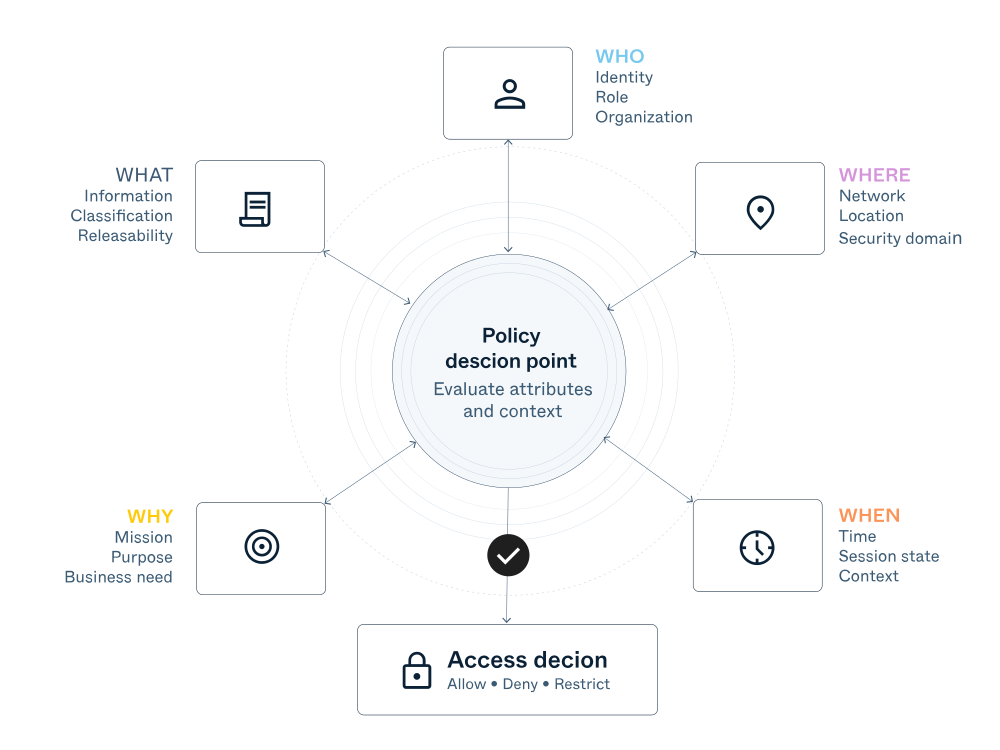
This idea sits at the heart of modern access control. It also requires an important distinction between authorization and trust.
- Authorization establishes what an identity is permitted to access based on verified attributes, roles, and entitlements.
- Trust is contextual. It considers whether that authorized participant should be allowed to access a particular resource, from a particular device, under the conditions that apply at that moment.
Modern access control looks beyond whether someone has the right credentials. It can evaluate the participant, device, information, and operating context together to determine whether access should be granted.
And that decision doesn't necessarily end when someone joins a session. Policy can be applied at admission and reevaluated at defined points during the session, allowing organizations to respond to changes in context and maintain an auditable record of access decisions.
Why traditional access control is changing
For many years, access control focused on the network. If a user connected from a trusted location, they were typically granted access.
That approach still works well in many environments. But organizations increasingly collaborate across departments, suppliers, agencies, and national borders. Participants often join from different networks while discussing the same sensitive information.
In these situations, deciding who should have access based on the network alone becomes increasingly difficult. Access decisions need to consider the participant, the information being shared, and the context of the session.
Data-centric security
Data-centric security shifts the focus from protecting the network to protecting the information itself.
Rather than asking "Is this connection coming from a trusted network?", it asks a different question:
Does this person have the right to access this information, in this situation, at this time?
Access decisions can take into account attributes such as security clearance, organizational role, nationality, mission assignment, location, or other policies defined by the organization. Because those policies are attached to the information rather than the network, they can be applied consistently wherever authorized participants connect from.
This approach is becoming increasingly important in coalition and multinational environments.
In September 2024, NATO ratified ACP240 (Allied Communications Publication 240), which introduces data-centric security as the architectural direction for coalition interoperability and identifies Attribute-Based Access Control (ABAC) as the preferred policy model. For organizations supporting NATO programs, it provides an important indication of where interoperability requirements are heading.
Where zero trust fits
Zero trust provides the broader security framework behind modern access control.
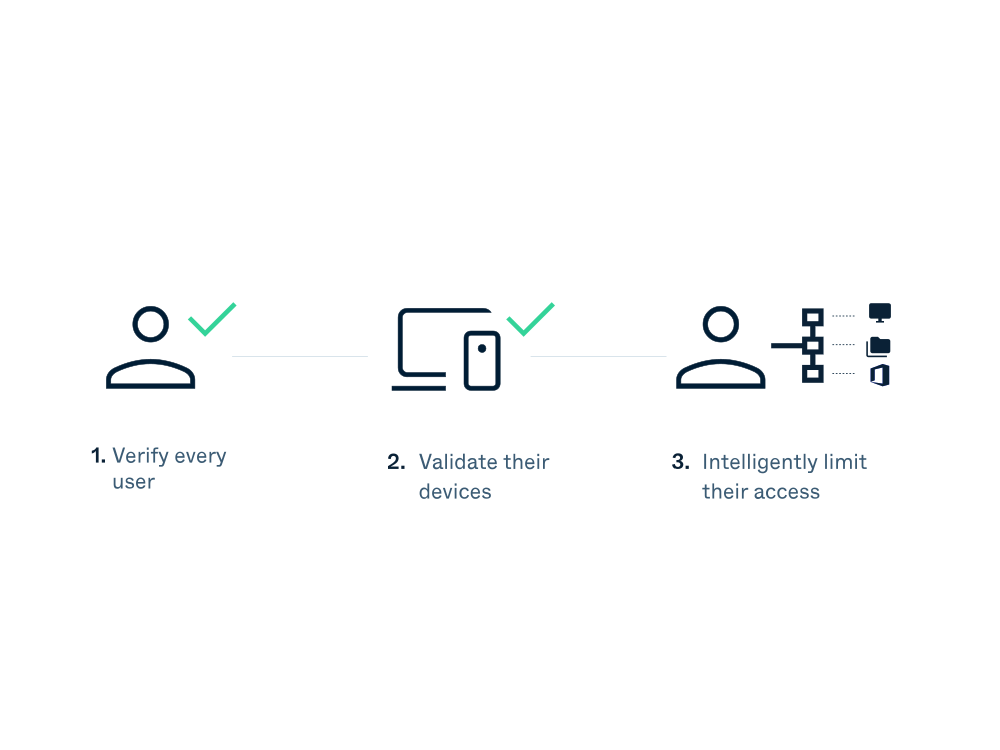
Rather than assuming users or devices are trustworthy because of where they connect from, zero trust requires every access request to be verified before access is granted.
In video communications, that means confirming each participant's identity, evaluating whether they should have access to the session, and applying the appropriate permissions throughout the meeting.
2. Choosing the right level of access control
The appropriate access controls depend on the sensitivity of the information being discussed and the potential consequences if that information is exposed. A routine internal meeting has very different security requirements from a healthcare consultation, a board meeting, or a classified operational briefing.
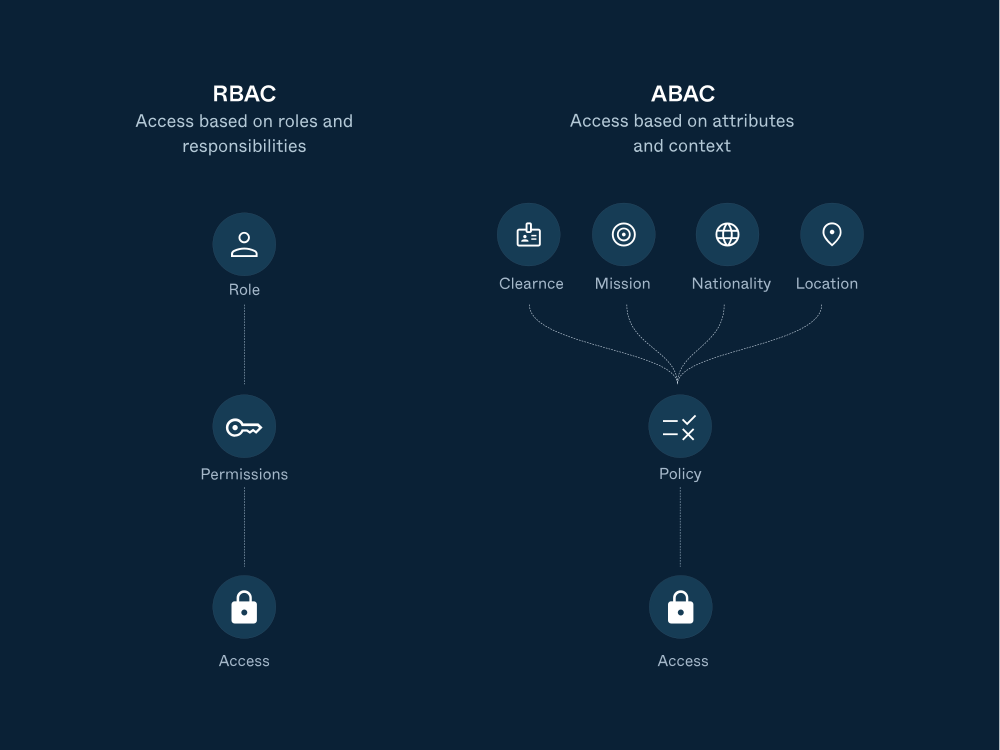
Many organizations use multiple levels of access control at the same time, combining different methods to address different risks. For example, Role-Based Access Control (RBAC) manages access based on established roles and responsibilities, while Attribute-Based Access Control (ABAC) can take into account changing factors, such as clearance, mission assignment, or location.
Layering controls in higher risk environments
Higher-risk environments typically rely on several complementary layers of protection. These controls address different risks and should be combined according to the information, operating environment, and consequence of failure.
Traditional controls such as passwords, multi-factor authentication, or meeting links remain important, but they do not determine what an authenticated participant is authorized to access. In higher risk environments, the layers of control may include:
RBAC and ABAC
RBAC establishes access based on defined roles and responsibilities, while ABAC adds need-to-know and mission-specific conditions such as clearance level, role, nationality, or assignment.
Cross-Domain Solutions (CDS)
Enable secure collaboration across different security domains while maintaining policy enforcement.
Liveness detection
Provides additional identity assurance by helping verify that a participant is physically present and who they claim to be.
Self-hosted or air-gapped deployments
Gives organizations greater control over infrastructure and data, while supporting sovereignty, segmentation, and resilience requirements.
Audit logging
Provides a record of access decisions and session activity for oversight, compliance, and investigation.
Cross-national intelligence briefing
Situation
Two allied intelligence services need to exchange classified intelligence during a joint briefing. Participants are joining from different organizations, countries, and secure networks, and not everyone should have access to the same information throughout the session.
Key challenge
Different participants require different levels of access based on their security clearance, organizational role, nationality, or mission assignment.
Access controls
- Attribute-Based Access Control (ABAC)
- Per-participant meeting links
- Cross-Domain Solution (CDS)
- Dynamic session labelling
Outcome
Each participant receives access based on the organization's security policy rather than the network they connect from. Information can be shared securely across organizations while maintaining appropriate classification controls throughout the session.
Coalition mission operations
Situation
Military units from multiple nations are coordinating an operation across headquarters, deployed locations, and mobile platforms. Participants may experience intermittent connectivity, operate from different security domains, and need to respond as the operational picture changes.
Key challenge
The communications platform must continue operating in demanding environments while maintaining security policies across coalition partners and changing classification levels.
Access controls
- Self-hosted or air-gapped deployment
- Attribute-Based Access Control (ABAC)
- Dynamic session labelling
- Secure identity management
Outcome
Organizations maintain operational control of their communications while ensuring access policies remain consistent across coalition participants, even in disconnected or highly restricted environments.
Government citizen services
Situation
A government agency is conducting sensitive video appointments with citizens, such as healthcare consultations, benefit assessments, asylum interviews, or legal hearings. Participants may be joining from personal devices over public internet connections.
Key challenge
The agency must verify participant identity while protecting sensitive personal information and maintaining a complete record of access where required.
Access controls
- Liveness detection
- Integration with trusted digital identity services
- Self-hosted deployment
- Comprehensive audit logging
Outcome
Citizens can access essential public services remotely while organizations maintain confidence in participant identity, protect sensitive information, and support compliance with regulatory and legal requirements.
Regional considerations
Although the principles of modern access control are consistent across industries and countries, the regulatory environment differs.

United States
FedRAMP and agency-specific security frameworks often shape deployment requirements.
Identity assurance is increasingly important for citizen services and judicial processes.

Europe
GDPR, eIDAS, and national sovereignty requirements often influence deployment choices.
Data residency and operational control are often key considerations for government organizations.
Access control throughout the session
In each of these scenarios, access control extends beyond the point when a participant joins. Policy can be applied throughout the lifecycle of the session:
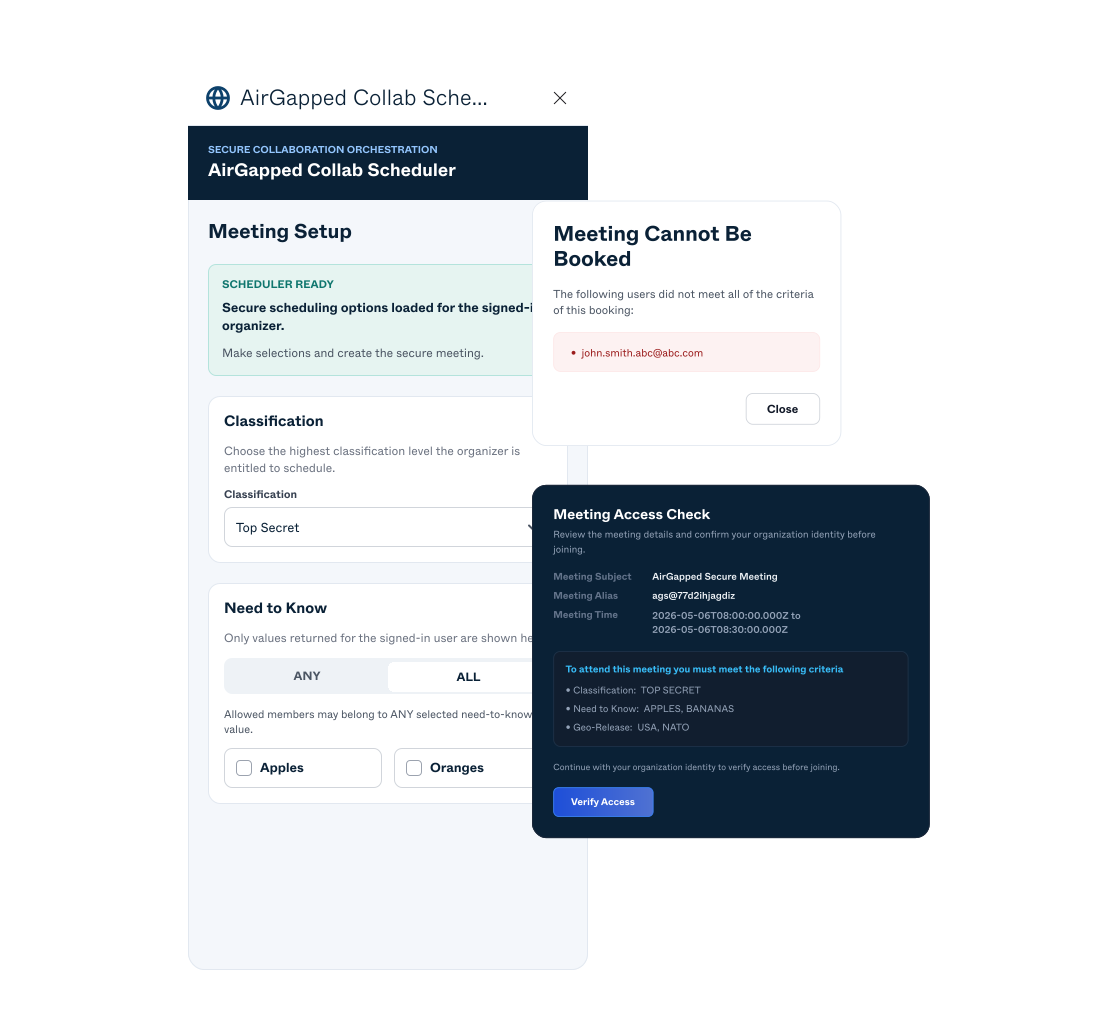
- At creation: The session can be associated with the relevant mission, classification, releasability, participant, and role requirements.
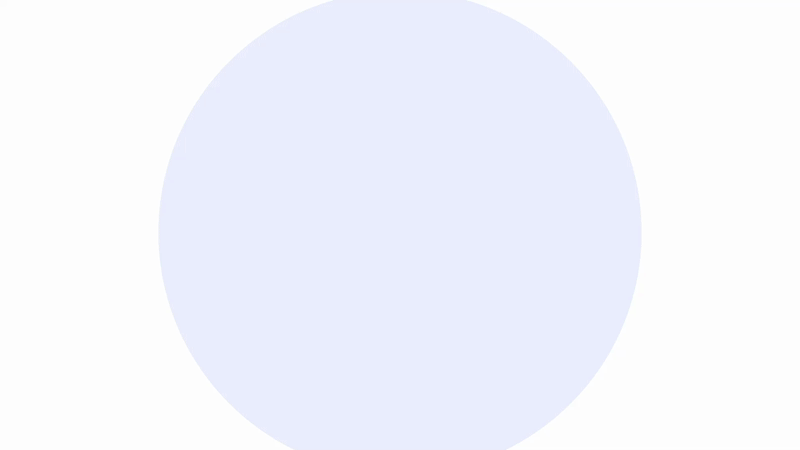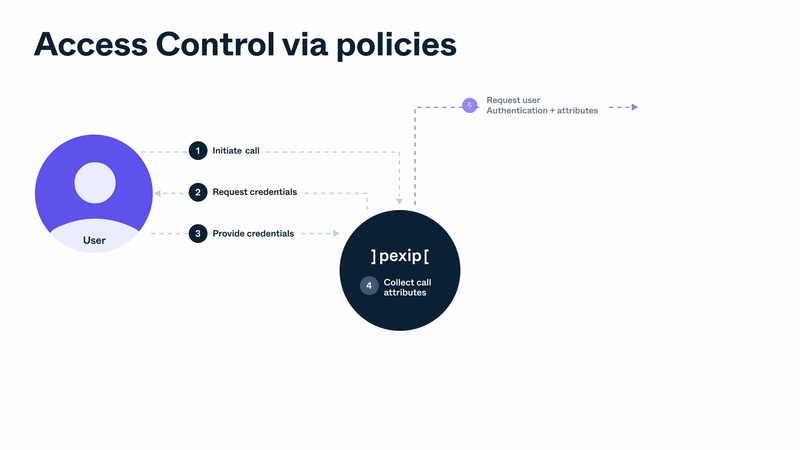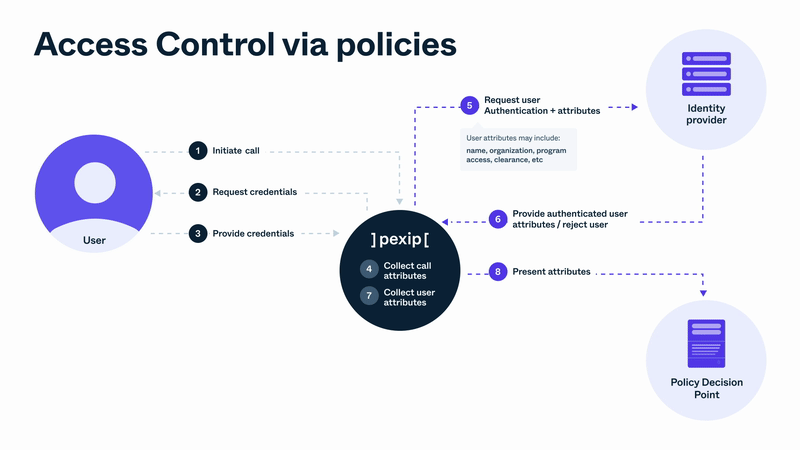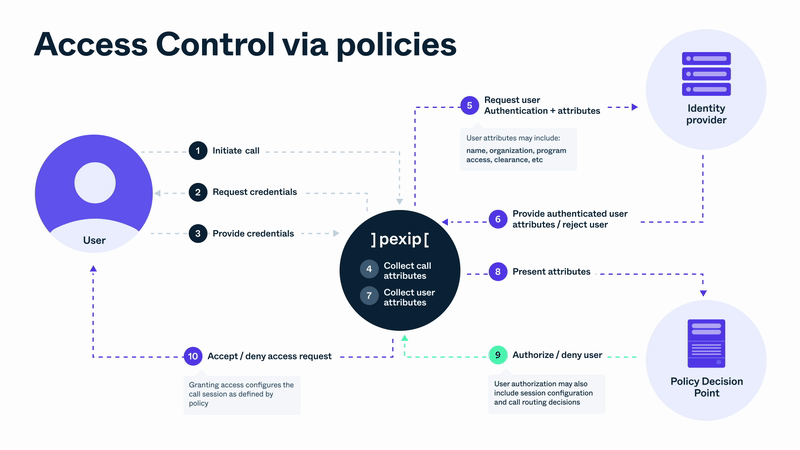
- At join: Current participant attributes are evaluated against policy to determine whether someone should be admitted, rejected, assigned a particular role, or directed to the appropriate session.
- During the session: Policy and activity can continue to be monitored and audited. If circumstances or access requirements change, participants can be removed, transferred, or moved to a differently protected session.
This allows security policy to remain aligned with the context of the communication, rather than becoming a one-time decision made when the meeting begins.
5. Building secure access with Pexip
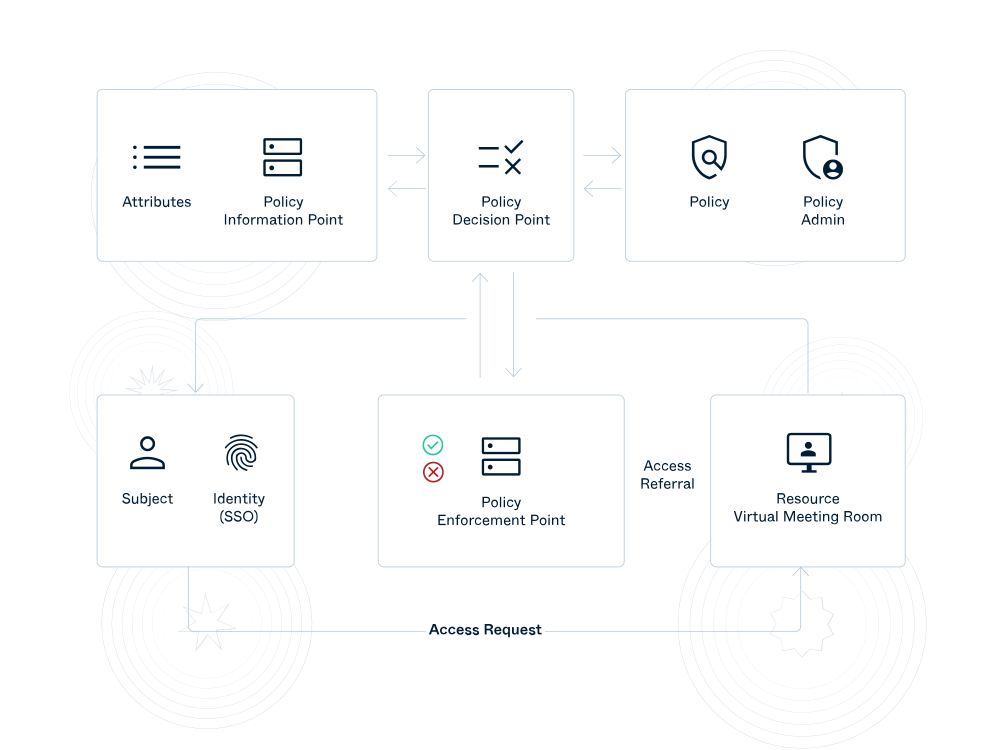
Modern access control relies on multiple technologies working together. Pexip fits within that existing security architecture, helping organizations turn identity and authorization policies into controls that can be applied to real-time communications.
Rather than requiring organizations to replace the systems they already use, Pexip can integrate with existing identity, RBAC and ABAC, scheduling, and other collaboration services. It provides the secure communications and interoperability layer that connects modern applications with existing communications environments.
Whether deployed in a sovereign cloud, private data center, or fully air-gapped environment, organizations can adapt Pexip to their security, sovereignty, and operational requirements while maintaining control over the wider architecture.
Identity and access
Pexip integrates with existing identity providers and policy services rather than duplicating them. Standards such as SAML 2.0 and OpenID Connect allow organizations to authenticate users through their existing identity management systems, while policy integrations enable authorization decisions to be applied to communications.
Organizations can combine multiple layers of access control, including:
- Single sign-on (SSO)
- Multi-factor authentication (MFA)
- Role-Based Access Control (RBAC)
- Attribute-Based Access Control (ABAC)
- Biometric verification and liveness detection
Pexip can integrate with external and local policy services, APIs, SDKs, plugins, and event data, helping organizations apply these controls within their existing security architecture.
Secure communications
Pexip supports secure meeting management through capabilities including:
- End-to-end encryption
- Per-participant meeting links
- Waiting rooms
- Dynamic session labelling
- Comprehensive audit logging
These controls help organizations protect sensitive information throughout the session lifecycle while supporting operational oversight and compliance requirements.